


Tokyo, Nov. 2 (Jiji Press)--Masatoshi Kumagai, chairman and group CEO of GMO Internet Group Inc., which has been mired in an unauthorized access incident involving its servers, said Monday that the company had failed to address security flaws flagged two years ago.
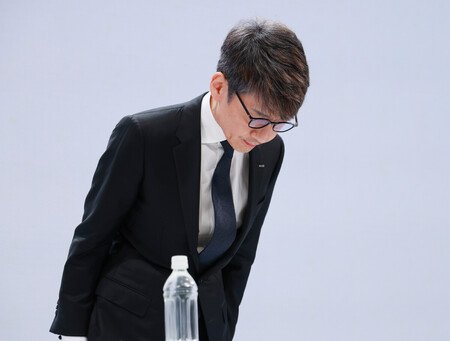
At the first press conference held by GMO since it announced the unauthorized access last month, Kumagai said, "We'd like to apologize from the bottom of our hearts to customers and related parties who suffered damage."
The company announced cuts in executive compensation the same day, including a 30 pct reduction in Kumagai's pay for three months.
At the press conference in Tokyo, the GMO group said that it was informed of system-related issues by experts from subsidiary GMO Cybersecurity by Ierae Inc. in April 2024. Kumagai acknowledged that the parent firm had failed to take sufficient measures after the warning, and said, "As the group's top representative, I take seriously our failure to make use of this feedback."
GMO said its measures were inadequate because it prioritized stable service operations and lacked the analysis needed to determine which security response should be prioritized across the group. The issue was not reported to Kumagai, and the cyberattack could not be prevented although the group carried out four emergency maintenance operations, it said.
[Copyright The Jiji Press, Ltd.]

 Read in other languages